Managed Backup Services With Isolated Storage and Tested Restores

Ventilated server cabinets in a data center.

Nightly backup emails coming back green do not tell you much on their own. If backup storage shares credentials with your production domain, or if nobody has tested a restore since last year, the gap usually shows up at the worst time. We set up, monitor, and verify isolated backups across databases, servers, file shares, and cloud mail tenants.

S3 Object Lock immutability Separated backup accounts PostgreSQL & SQL PITR M365 & Workspace backup

Keeping Backups Intact When Primary Accounts Are Compromised

In the event of a ransomware incident or a stolen cloud session, it is not unheard of for attackers to go after the backup system right alongside production. When a local backup server joins the same Active Directory domain as the rest of the company, or when cloud snapshots sit inside the same AWS account as the application, one compromised administrator role can wipe out both copies together. Having an offsite copy matters, though location alone is not sufficient.

So how do you protect backups when primary credentials do get stolen? Wherever practical, we put recovery vaults and KMS encryption keys under separate administrative control so the systems and roles used in production cannot overwrite or delete them. In the cloud, S3 Object Lock in Compliance mode enforces WORM (write once, read many) retention; on premises, hardened Linux XFS repositories outside Windows domain control handle fast local restores. Read our immutable 3-2-1 backup guide for how those pieces fit together.

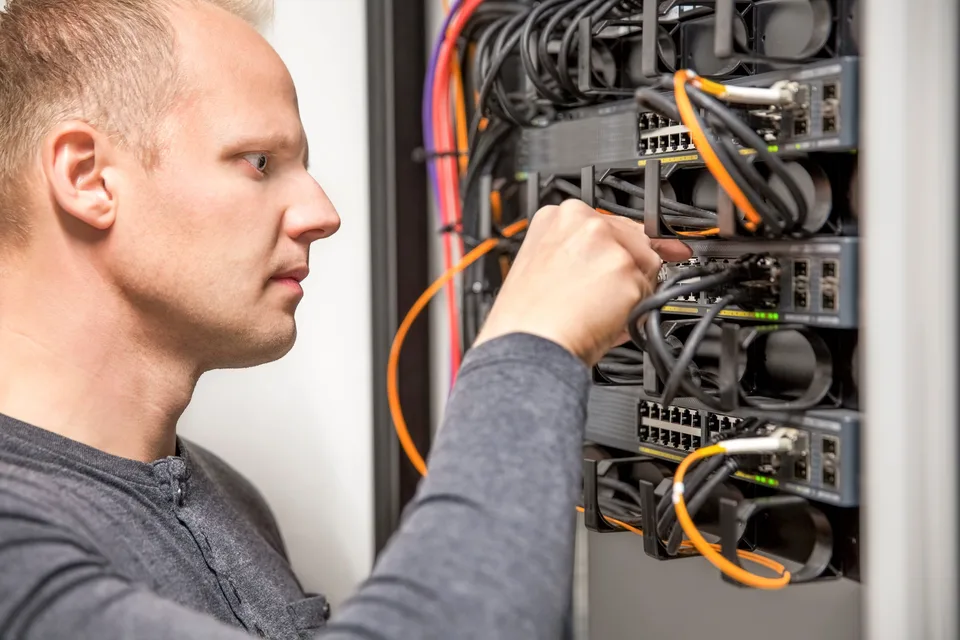
Network engineer connecting a dedicated fiber optic uplink inside a rack switch.

Separated Accounts & Encryption Keys

Offsite vaults, KMS keys, and backup orchestration run in an isolated cloud account or separate security tenant gated by independent hardware-MFA credentials. Compromising a production role does not hand over the vault.

Immutable Local & Cloud Repositories

Cloud vaults enforce WORM retention locks, while local recovery appliances run hardened Linux XFS storage off the Windows domain so multi-terabyte LAN restores do not wait days on an internet circuit.

Daily Alerting & Engineer Follow-Through

A stalled transaction-log archive, a failed snapshot, or an unexpected jump in backup size opens a ticket directly for our engineers rather than sitting unread in a shared inbox.

Backup Coverage Across Databases, Servers, and SaaS Tenants

A file-level backup agent copying open database files on disk will happily capture a half-written state, and cloud recycle bins do not stop tenant-wide deletion. We match the capture method to how each workload actually writes data.

Workload CategoryCapture MethodRecovery GranularityStorage Isolation
Relational Databases
PostgreSQL, MySQL, MariaDB, SQL Server
Consistent base snapshots (pgBackRest, Percona, RDS/Aurora, VSS) plus continuous WAL, binlog, or transaction-log archiving Point-in-time recovery prior to an accidental table drop or bad migration Cross-account encrypted snapshots and Object-Locked log archives
Cloud & Local Virtual Machines
AWS EC2, Azure VMs, VMware, Hyper-V
Application-consistent changed-block snapshots and AWS Backup Vault Lock policies Full VM boot, volume attach, or individual file and folder extraction Hardened local Linux repository paired with offsite immutable object storage
Microsoft 365 & Google Workspace
Mailboxes, SharePoint, OneDrive, Shared Drives
Automated incremental API capture independent of native Microsoft and Google retention bins Individual messages, calendars, SharePoint libraries, permissions, or departed-staff archives Encrypted external vault outside the primary Microsoft 365 or Workspace tenant
NAS, File Shares & Object Buckets
SMB/NFS shares, CAD libraries, S3
Deduplicated chunked snapshots and cross-region versioned object replication Single-file revision or directory rollback without restoring multi-terabyte volumes Append-only repositories with locked retention policies

Controlling Retention Costs, Testing Restores, and Planning Failover

Storage economics

Predictable Retention Lifecycle Rules

Forgotten cloud snapshots have a way of doubling storage bills quietly over a year or two. Pushing recent backups straight into deep glacier tiers creates the opposite problem: multi-hour retrieval delays and per-gigabyte fees right during an outage. We keep 14-to-30-day operational chains warm and age multi-year compliance archives down cleanly.

Read the 3-2-1 backup guide
Verification

Scheduled Test Restores & Evidence

A completed backup job only proves that blocks were written somewhere. On an agreed schedule, we restore backups onto isolated test instances, replay transaction logs, run database read checks, and record elapsed timings along with anything that tripped up the restore.

Build a restore test checklist
Full-service continuity

When You Also Need Standby Failover

Managed backups make sure clean data survives to recover. What if the business cannot wait hours to stand up fresh servers and repoint traffic when a primary region fails? When recovery windows are tight, pair isolated backups with standby compute, DNS failover, and tested runbooks.

See disaster recovery services

How Ongoing Backup Management Works

First

Workload & Retention Mapping

Catalog databases, virtual machines, file shares, encryption keys, and SaaS tenants, then match backup intervals and lock durations to both daily operations and regulatory retention rules.

Second

Isolated Vault Provisioning

Stand up separated storage accounts, KMS keys, immutable retention locks, and local Linux repositories while keeping existing backup jobs active until baseline seeding finishes.

Third

Daily Monitoring & Restore Checks

Investigate failed or stalled jobs every day, trim orphaned snapshots as data grows, and hand over dated test-restore reports for leadership, auditors, or cyber-insurance renewals.

Questions About Managed Backup Services

Doesn't Microsoft 365 or Google Workspace already back up our email and files?

Microsoft and Google replicate storage so their own hardware failures do not lose data, though your organization remains responsible for what happens inside your tenant. Native recycle bins and version histories do not replace an independent backup if a compromised admin account purges mailboxes, ransomware syncs encrypted folders to OneDrive or SharePoint, or a departed employee's license is removed early.

What happens if S3 Object Lock Compliance mode is set for too long?

In Compliance mode, nobody can delete a locked object version before its clock runs out—not even the cloud account root user—so storage charges continue until retention expires. That is why we size rolling operational locks carefully, often 14 to 35 days on active recovery chains, and align longer archival tiers with deliberate legal and regulatory retention policies.

Who owns the backup storage accounts and encryption keys?

Either ownership model works. We often build isolated vaults inside dedicated AWS or Azure member accounts owned by your company with separate break-glass credentials, or we can store encrypted backups on briskData-managed repositories. Account ownership, key custody, and export steps are written down before onboarding begins.

Can you take over monitoring of our existing Veeam or AWS Backup setup?

Yes. Taking over an existing Veeam, AWS Backup, Azure Backup, pgBackRest, Percona, or NAS setup is common. We check whether backup storage still shares domain or cloud admin credentials with production, separate those roles where needed, and take over daily failure triage and scheduled restore checks.

Review Your Backup Coverage

Tell us which databases, servers, file shares, or cloud mail tenants need protection, approximate data volume, and any retention requirements.

  • Isolated backup credentials and S3 Object Lock immutability
  • Application-consistent coverage for databases, VMs, and M365 or Workspace
  • Daily failure monitoring and documented restore verification

Available as a focused backup modernization project or as part of ongoing managed IT and cloud operations.

Review Your Backup Coverage

An NDA is available before you share sensitive details. You can request one in your message.

Your message goes directly to an engineer.

Privacy policy · No passwords or sensitive files, please.